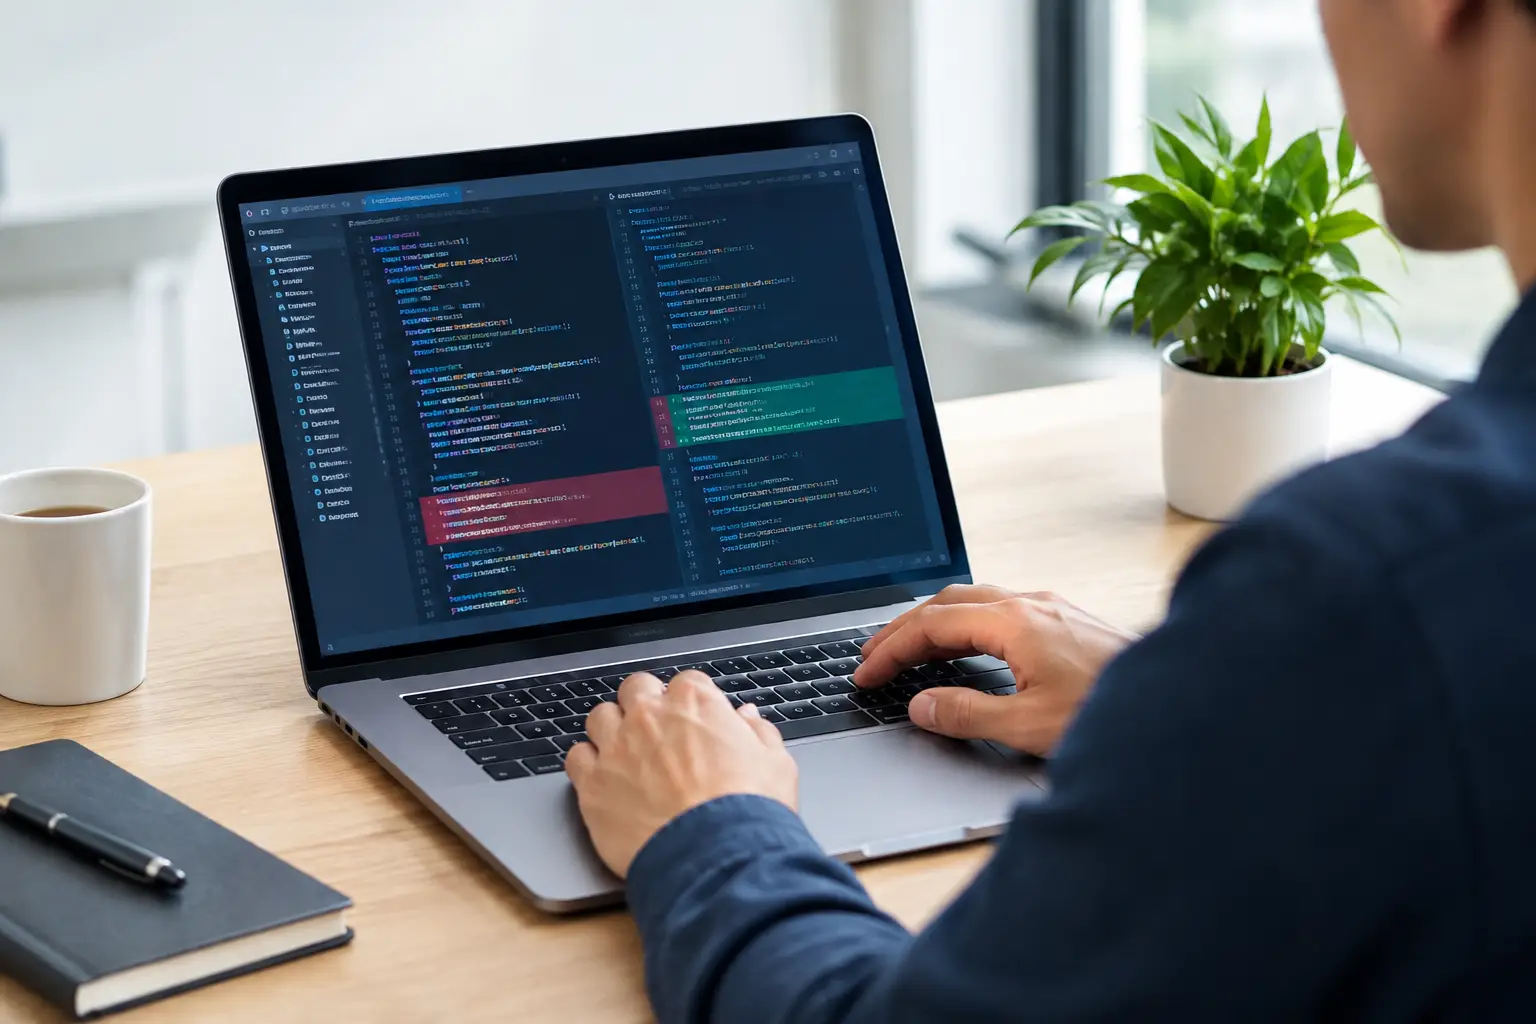
A pull request that waits two days for review is not just an engineering delay. It can hold up a customer fix, a compliance update, a mobile release, or a revenue-critical feature. The best AI code review tools help teams shorten that wait without treating software quality as an afterthought. They surface likely defects, security issues, missing tests, and maintainability concerns while human reviewers focus on architecture, product behavior, and business risk.
For founders and technology leaders, the value is straightforward: faster feedback can improve release predictability. But an AI reviewer is not a substitute for experienced engineering ownership. The right tool depends on your repository, delivery workflow, security requirements, and the kinds of mistakes your team needs to catch repeatedly.
What AI Code Review Should Actually Improve
A useful AI code review tool works inside the pull request workflow your developers already use. It reads the code change in context, leaves specific comments, and explains why a pattern may be risky. The strongest results come from tools that reduce repetitive review work, rather than tools that produce a long list of generic observations.
For a healthcare portal, this may mean flagging unsafe handling of patient data or weak authorization checks. For an e-commerce platform, it may mean identifying an edge case that affects payment totals, inventory updates, or discount logic. In a workflow automation product, it could catch a race condition before it creates duplicate records.
Teams should expect AI review to help with code readability, defect discovery, security scanning, test suggestions, and adherence to agreed coding standards. They should not expect it to reliably understand every business rule from a ticket or make a final decision on a high-risk change. Context still matters. A technically correct refactor can be the wrong product decision, and a secure-looking change can still violate a business process.
Best AI Code Review Tools for Product Teams
The tools below are strong options for different delivery environments. A short pilot on real pull requests will tell you more than a feature checklist, especially when your codebase includes legacy services, custom workflows, or multiple languages.
GitHub Copilot Code Review
GitHub Copilot Code Review is a practical choice for teams already running their delivery process in GitHub. Its main advantage is proximity: developers can request review feedback where they create pull requests, without adding a separate review destination.
It can identify suspicious logic, potential bugs, and improvements to clarity while offering comments in a familiar collaboration flow. This makes it a sensible starting point for startups and distributed product teams that want to increase review coverage quickly.
The trade-off is that repository-native convenience does not automatically create a complete quality program. Teams still need branch protections, test automation, security checks, and clear reviewer accountability. It is most effective when developers give it useful repository context and treat its feedback as a first-pass signal, not an approval authority.
CodeRabbit
CodeRabbit is built around pull request reviews and is often a good fit for teams that want detailed, conversational feedback on each change. It can summarize pull requests, identify potential issues, suggest improvements, and respond to follow-up questions in the review thread.
For a growing engineering team, this can reduce the time senior developers spend explaining routine concerns. It is particularly useful when pull requests span several files and reviewers need a quick explanation of what changed before assessing implementation details.
The risk is comment volume. If the configuration is too broad, developers can receive more feedback than they can reasonably act on. Start with high-confidence findings and team-specific guidelines, then adjust rules based on false positives and the issues that actually reach production.
Snyk Code
Snyk Code is a strong option when application security is a major buying criterion. It focuses on code-level vulnerabilities and can help teams identify insecure patterns early, before they become deployment issues. For organizations handling customer data, payments, health information, or enterprise integrations, security feedback during development is far less expensive than remediation after release.
Snyk Code works best as part of a broader security approach that also examines open-source dependencies, containers, cloud configuration, and runtime controls. Its AI capabilities can help prioritize and explain findings, but the real value comes from integrating security checks into engineering decisions instead of leaving them for a final audit.
SonarQube and SonarQube Cloud
SonarQube has long been a familiar name in code quality management, and its AI-assisted capabilities help teams address issues more efficiently. It is especially useful for organizations that need measurable quality gates across multiple repositories, languages, and development teams.
Its strength is disciplined standardization. Product leaders can establish expectations around reliability, maintainability, duplication, security hotspots, and test coverage, then make those expectations visible before code is merged. That is valuable for enterprise modernization projects where a new service must coexist with older systems.
SonarQube may feel more process-driven than a conversational pull request assistant. That is often a benefit for regulated or large-scale environments, but smaller teams should avoid turning every minor code-style issue into a release blocker. Use quality gates to protect meaningful standards, not to create friction.
Qodo Merge
Qodo Merge is designed to bring AI-generated review feedback, test ideas, and pull request analysis into the development workflow. It is useful for teams that want the AI to go beyond style comments and engage with expected behavior, edge cases, and test coverage.
This can be valuable for MVP teams moving quickly. Early-stage products often change fast, and test suites may not yet cover the full range of user scenarios. Qodo Merge can prompt developers to consider conditions they may have missed, such as empty states, invalid inputs, retries, permission boundaries, and failure handling.
As with any generative tool, its suggestions need verification. A generated test can pass while testing the wrong behavior. Engineering leads should review whether AI suggestions reflect the intended product requirement, not simply whether they compile.
GitLab Duo Code Review
GitLab Duo Code Review is worth evaluating for organizations that use GitLab for source control, CI/CD, and planning. Its appeal is similar to GitHub Copilot’s: review assistance is closer to the place where teams already manage merge requests and delivery pipelines.
For teams that want fewer disconnected tools, that integration can simplify adoption and reporting. It can also support a more consistent workflow from issue to merge request to deployment. The best fit is typically a GitLab-centered organization that values platform consolidation and already has well-defined pipeline controls.
Before standardizing on it, validate language support, deployment options, and how it handles the frameworks your team uses. The right native tool is only an advantage if it provides useful feedback on your actual code.
Amazon CodeGuru Reviewer
Amazon CodeGuru Reviewer is most relevant to teams with substantial AWS usage. It can analyze code for quality and performance concerns, with particular relevance to cloud-based applications and services.
For a platform with Lambda functions, AWS SDK integrations, or high-volume backend processing, performance observations can be as important as basic bug detection. A small inefficiency can become a material cloud cost when it runs millions of times.
Its cloud alignment is also its limitation. It is less likely to be the universal answer for a mixed environment that is not closely tied to AWS. Choose it when its infrastructure context provides real operational value, not simply because it includes AI.
How to Choose an AI Reviewer Without Creating Noise
Start with the failure modes that cost your business the most. If production incidents come from authorization mistakes, prioritize security and data-flow analysis. If your bottleneck is slow pull request turnaround, prioritize review summaries, actionable comments, and collaboration features. If technical debt is affecting delivery speed, look for quality gates and maintainability reporting.
Then run a controlled pilot. Choose one or two active repositories, define what success looks like, and review results after several sprints. Useful measures include pull request cycle time, number of high-severity findings caught before release, false-positive rate, reviewer satisfaction, and escaped defects. Do not judge a tool by the number of comments it produces.
Data governance deserves equal attention. Ask where source code and prompts are processed, whether customer data can be retained, which access controls are available, and whether the vendor supports your compliance requirements. Enterprises may need private deployment options or stricter repository permissions. A tool that improves review speed but creates an unacceptable IP or compliance exposure is not the right tool.
Finally, establish a clear operating model. AI can comment on every pull request, but named engineers should remain accountable for approval. High-risk changes involving authentication, payments, personal data, database migrations, or core business rules should receive mandatory human review regardless of an AI recommendation.
Make AI Review Part of Delivery Discipline
The best results come when AI review supports a complete engineering system: clear requirements, thoughtful architecture, automated tests, CI/CD checks, peer review, monitoring, and post-release learning. It should help developers spend less time spotting repeatable mistakes and more time making sound product decisions.
At Xornor, we see this balance as essential to dependable delivery. AI-assisted review can accelerate feedback, but reliable software still requires engineers who understand the business outcome behind the code. Start with a focused pilot, tune the tool around the risks that matter to your product, and keep human ownership where the consequences are highest. Get in Touch when you need a delivery team that can build those quality controls into your product from the first release.